Cybersecurity
Strengthen network and system security with secure connectivity and access control.
Reduce cyber risk across connected networks, systems and data. 7SCSC integrates firewalls, network segmentation, secure remote access and device hardening to help prevent unauthorized access and support reliable operations.
- Site focused
planning - Connected
systems - Ongoing
support
The operational challenge
What the system needs to solve.
Exposed services, weak access controls and unsegmented networks can leave business and operational systems vulnerable to unauthorized access. Security controls should reflect the people, devices and data that need to connect.
Systems & applications
Choose the system around the job.
Explore the equipment and applications we can assess for your project. Your proposal defines the selected products, supported functions and installation scope.
Firewall and network separation
Separate users, cameras, guest access and building devices into appropriate network zones. Define necessary connections explicitly and retain a documented change process.
- Typical equipment
- Firewalls, managed switches and network policy
- Where it fits
- Offices, CCTV systems and command networks
Secure remote and branch access
Scope VPN or supported zero trust access around named users and devices. Limit vendor maintenance access to approved systems and operating windows.
- Typical equipment
- Remote access gateway, identity and device controls
- Where it fits
- Branches, field support and remote operators
Endpoint protection
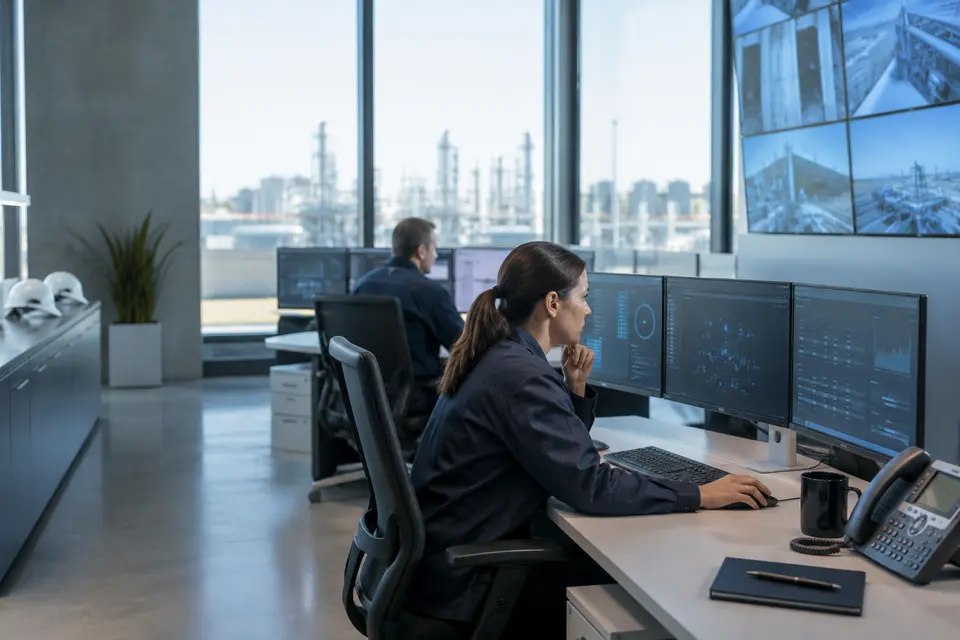
Protect servers and operator computers with compatible endpoint prevention and detection tools. Decide who reviews alerts and how a suspected device is isolated.
- Typical equipment
- Endpoint licenses, management console and response process
- Where it fits
- Staff computers and control room workstations
Monitoring and operational hardening
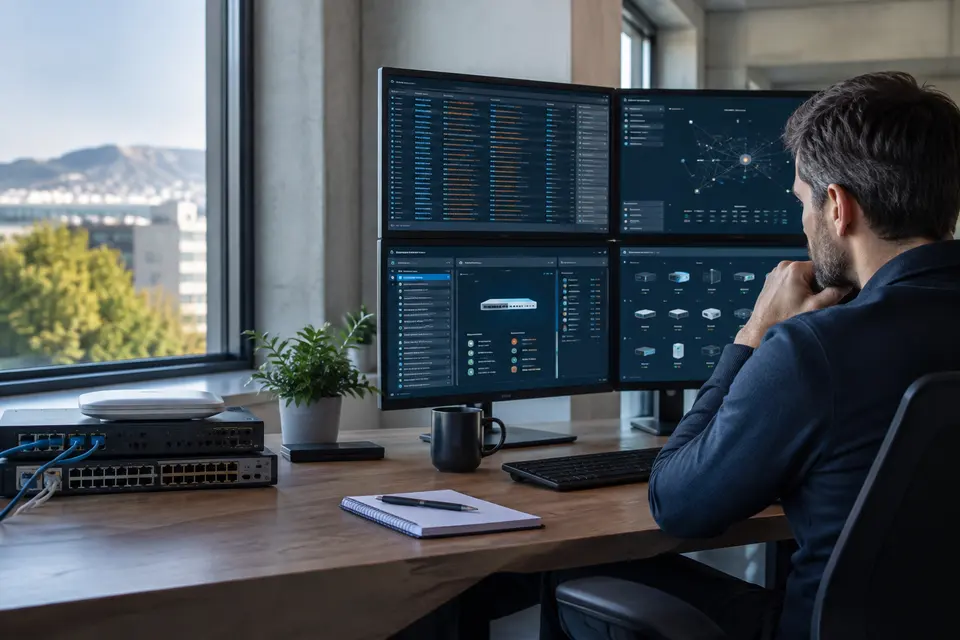
Review firmware, credentials, logging and configuration recovery for the deployed systems. Schedule maintenance and incident escalation instead of relying on a firewall alone.
- Typical equipment
- Central logs, configuration backups and asset inventory
- Where it fits
- New installations and existing security infrastructure
Functions, equipment & operation
Protect the infrastructure behind video and connected sites.
Explore the functions and design options below. The final components, licenses and integration scope are confirmed against your site requirements.
Network zones and access rules
Separate camera, server, operator, guest and management traffic where appropriate. Document required communications and define firewall rules around those flows.
Remote access and identity
Scope controlled VPN or approved remote access, individual administrator accounts and supported multi factor authentication. Define account removal and vendor access periods.
Hardening, logs and recovery
Review exposed services, firmware update procedures, configuration backups and relevant security logs. Assign responsibility for investigating alerts and restoring configurations.
What makes up the system
- Firewall and supported remote access services
- Managed network equipment and identity services
- Log collection and monitoring tools as scoped
- Configuration backups and recovery documentation
How the project works
- 01Inventory assets and required connections
- 02Design security zones and access policies
- 03Apply controls and test permitted workflows
- 04Document monitoring, updates and recovery
What we confirm before implementation
- Existing network dependencies and downtime windows
- Supported identity and logging integrations
- Incident ownership and managed service scope
Share your current equipment, site layout and operational priorities so the proposal can identify included functions, optional integrations and acceptance criteria.
In practice
Where it fits
Plan cybersecurity around your environment, equipment and the people who use it.
- CCTV and IoT networks
- Remote maintenance access
- Command center and enterprise infrastructure
Connected systems
for real impact
How it connects
- 01Asset and access review
- 02Network boundaries
- 03Firewall / VPN
- 04Hardened devices
- 05Operational review
Technology shaped around your operation
Published scope
Supporting information
Supporting company information
Network security ↗Published technology references
Referenced products and compatibility are confirmed for each project. Source inclusion is not a claim of authorized partnership.
Sangfor ↗Questions about Cybersecurity
Is 7SCSC developing its own security software?
This service integrates suitable third party security products and configuration practices. No proprietary security platform is claimed.
Does a firewall alone secure the installation?
No. Accounts, updates, segmentation, remote access and operating practices all matter. The scope is agreed around the existing environment.


Project requirements
Discuss Cybersecurity requirements
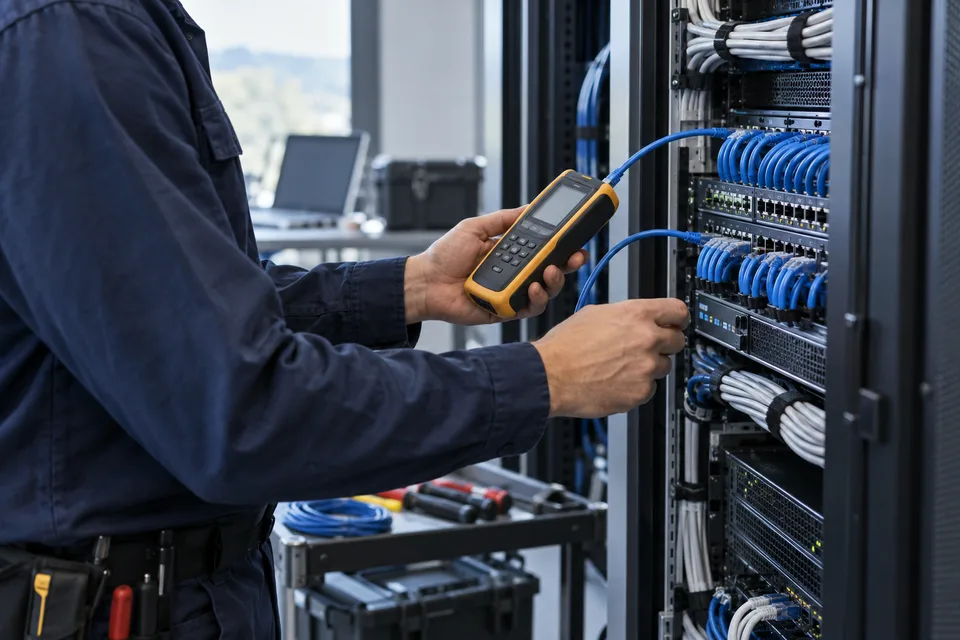
Include the site location and existing equipment. Use the review points to prepare your inquiry.
Include in your inquiry
- Existing network dependencies and downtime windows
- Supported identity and logging integrations
- Incident ownership and managed service scope